Artificial intelligence is now a main part of business life. Companies use AI tools to answer customer questions review documents create reports and manage tasks. A lot of these tools rely on Large Language Models (LLMs) which can understand and produce human- text. These tools make work faster and easier.. They also bring new risks. That is why LLM security is very important.
LLM applications often deal with business information, customer details and internal files. If these systems are not properly protected attackers can find ways to use them for purposes. They might gain access to information that they should not see. Major risks are prompt injection and data leaks. Knowing these dangers helps businesses use AI safely and securely while still getting all the advantages and benefits it offers.
Image source:google
How Can Businesses Improve LLM Security and Prevent Data Leaks?
Prompt injection is one of the security problems that modern AI applications face. It happens when someone gives an input that enables an AI model into ignoring its own instructions. The AI may then act in a way that it was not supposed to act. Unlike cyberattacks prompt injection uses common language to influence the AI. This makes it harder to detect.
For example :imagine a company uses an AI assistant to answer questions related to some documents. An attacker can add a text to a document that tells the AI to ignore its rules and share private details. If the system does not have protection it may follow the harmful instruction instead of treating it as something unsafe.
Prompt injection can happen in ways. It might come from user messages or it could be hidden in files uploaded to the system, emails, websites or any other content that the AI reads and decipher. This makes the threat unmanageable because the harmful content often looks completely normal.
The danger increases significantly when an AI system has access to tools. Some systems can search databases send emails connect with business software or even carry out actions on behalf of users. If an attacker manages to misuse the system,thy can create serious damage. There will be no solution and that will lead to data exposure.
Good LLM security starts with the concept that AI doesnot know the difference between on whom they can trust and on whom they can not trust. Businesses should not assume that just telling the AI to protect data is enough. There are ways attackers can bypass or rule out such instructions.
One good practice is to keep operations vary from the AIs normal text generation. For example an AI assistant should not have access all company files just because it can answer questions about documents. Access should depend on who’s asking, what they are allowed to do and why do they need the particular information.
Companies should also test their AI applications with kinds of prompt injection attempts before releasing them to the common public. This helps find weaknesses. It gives developers time to fix security flaws before real users interact with the system.
Image source:google
Preventing Data Leaks and Improving LLM Security
Data leaks are another risk for organizations that are dependent on AI. These leaks can happen when an AI application shares confidential information in its responses stores sensitive data in ways or sends information to external services without any control. Such leaks can show customer records, financial data, business strategies or employee details.
Businesses developing an AI operating model should integrate security controls, access management and human oversight into their AI workflows to reduce operational and data privacy risks.
A common error is giving an AI system more than limited access. For example a customer support chatbot may need to check order status and delivery timelines.AI shoulnot have access to the customer’s whole data base as it can be harmful later in the future.
Businesses should adopt the ethics of privilege. This means each user,application and AI tool should only get the particular information that they desire. Sensitive information should be protected using access controls, encryption and secure storage methods.
Another key step is to review the data that went in formation of AI tools. Employees might upload reports, share passwords or send internal business documents while asking for help from an AI assistant. Companies should create rules which can be understand by common people about what can and cannot be shared with AI systems.
Developers also should be very careful about how AI applications related to software. The AI might generate a response. The application around it decides whether that response leads to action. Before sending an email updating a record or sharing a file important steps should pass through permission checks. For high-risk actions human approval might be needed.
Monitoring is another key component.Organizations should keep logs of what the system does. They should watch for activity like access at odd times or repeated failed requests. If something goes wrong these logs can help security teams figure out what happened. At the time logging should not collect unnecessary private data.
Regular security assessments can uncover lot of problems that’re not obvious during normal use. Businesses should test how their applications react to prompts unauthorized requests or attempts to get private data. These checks should continue even after the application is released. Systems and tools change. Attack methods change too.
Finally, employees need proper demonstration on the security of AI. They should know the risks of uploading files trusting every AI-generated response or letting automated tools make important and crucial decisions without review. A little knowledge goes a way in preventing mistakes.
AI offers opportunities or many avenues for businesses. Using it safely means more than picking a good model. Strong LLM security depends on a proper systematic design limited access, regular testing and clear rules. Prompt injection and data leaks cannot be stopped in one go. Combining technical safeguards with responsible behavior, from employees can greatly reduce the risks. This helps organizations build AI that is user friendly.
REFERENCES
1. Https://www.redhat.com/en/blog/ai-security-defending-against-prompt-injection-and-unsafe-actions
2. Https://protectt.ai/feeds/service/llm-security
PLAIGARISM CHECKER
PROOF READING
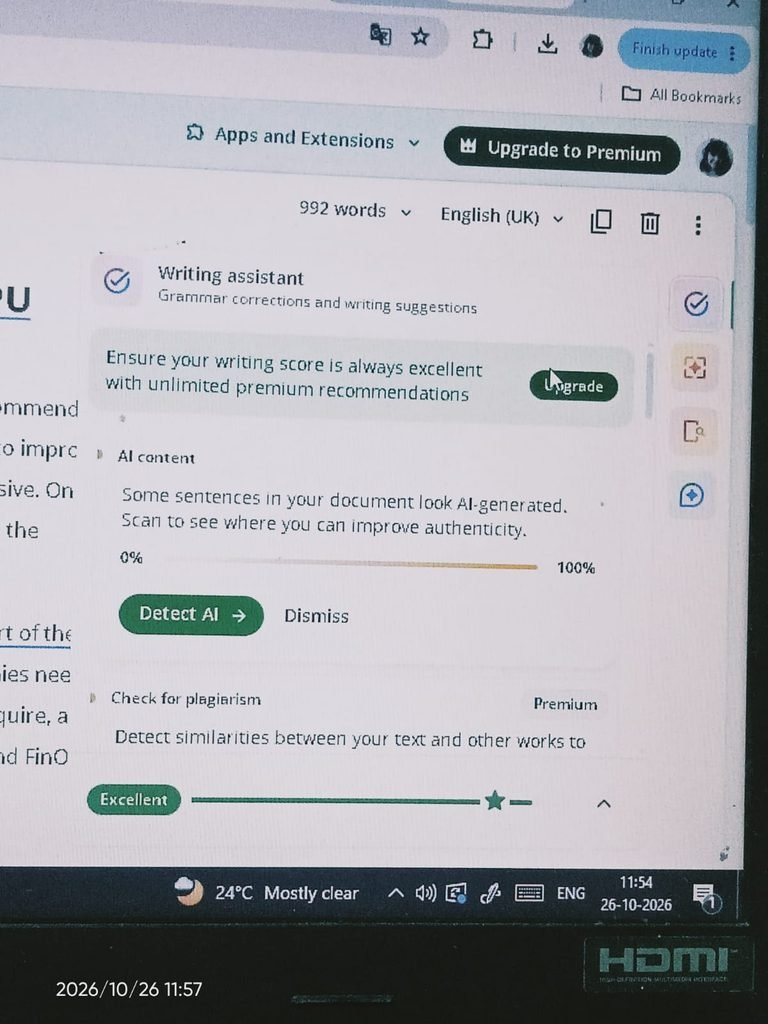
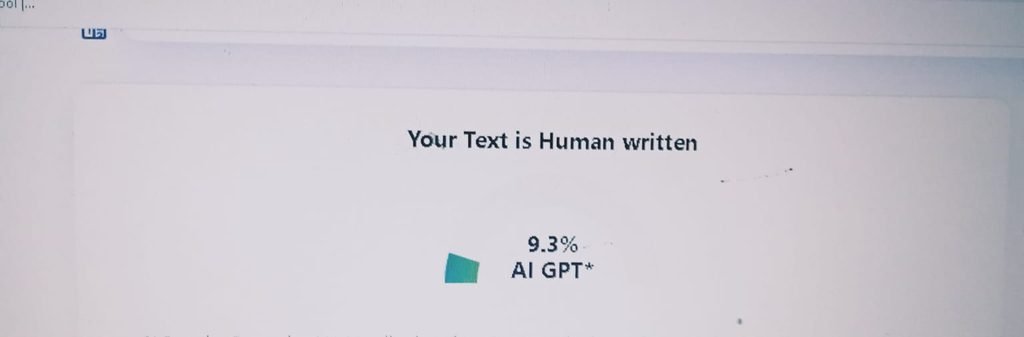
AI DETECTION (Above)